SYSTEM_LOAD // 0xDEADCLICK ANYWHERE TO ENTER ›
L LAWLIET // INVESTIGATOR CODEX
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠛⠋⠉⠉⣨⣽⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠁⠀⠀⠀⠀⣠⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⠋⠀⠀⠀⠀⠀⠀⠰⠟⠻⠛⠛⠛⠻⠿⠿⢿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⠿⠿⠛⠛⠋⠉⠉⠉⠙⠃⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠉⠙⠻⢿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠟⣋⣀⣤⣤⡤⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣩⣼⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢤⣤⣶⣾⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⠏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⢿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠻⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠀⠀⠀⢀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣃⡔⠀⠀⠀⠀⠀⡰⠊⠡⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢹⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠠⡐⠁⠀⢀⠡⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿
⣿⣿⣿⣿⣿⡟⠁⠀⠀⠀⣠⢷⠀⢿⣟⣿⡇⠂⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢻⣿⣿
⣿⣿⣿⠿⠋⠀⠀⠀⠀⣼⣻⣎⣧⡬⢭⣞⣬⡀⠀⠀⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠸⣿⣿
⣿⣿⣤⣤⣤⣤⡄⠀⠀⣿⣳⡿⠃⣽⣟⣾⣳⠇⠀⠀⠆⠣⠀⠀⢀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿
⣿⣿⣿⣿⣿⣿⣷⠀⠀⢹⣯⢿⣷⣻⣞⡷⣿⢷⢠⠃⠀⠀⣀⠠⣟⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣤⣀⡀⠀⠙
⣿⣿⣿⣿⣿⣿⣿⡆⠀⠀⢿⣇⣈⣷⣿⣻⣽⣯⢷⠈⢟⣿⣻⠶⠈⠖⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢰⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠏⣰⠀⠀⠈⣿⢿⣹⣾⡿⣷⣏⡿⣆⠀⠈⠁⣀⠾⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⣿⣿⠟⣡⣾⣷⠀⡀⢳⣌⠛⢫⣿⡽⣟⣾⡽⣾⡽⣶⣻⡜⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⡿⠃⣼⣟⡷⣷⣾⣷⠘⣾⣿⣦⡈⠙⠛⠷⠿⢳⡿⠷⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣴⣄⠀⠀⠀⣿⣿⣿⣿⣿
⣿⣿⢁⣾⣻⢾⡽⣯⣿⣽⡆⣿⡿⠿⢏⣷⡠⡂⠄⡄⠀⠀⠀⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣷⣤⣀⣘⣿⣿⣿⣿
⣿⠁⣾⣷⠯⠿⠽⠿⠟⠋⢑⡵⣮⢟⡾⣶⠝⠆⠀⠀⠠⣾⣹⡟⣿⣳⣄⠀⠀⠀⠀⢠⣶⡀⠀⠀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠇⢸⢆⣠⣴⣶⣶⣶⡞⢡⡾⠉⠈⠉⠉⠁⠀⠀⠈⠀⠀⠀⠉⠛⠓⠓⢋⡀⠀⠀⢠⣿⣿⣷⣦⣀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠀⣴⣿⣟⣯⢿⣞⣿⠀⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠄⠀⠘⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿
⡄⠻⣿⣟⡾⣯⢿⠟⡄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠐⠠⢠⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡟
⣿⣦⠉⣉⠹⠩⠥⠛⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢲⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⡭⡻⠇⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⣮⣞⡍⠆⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⣿⣼⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣧⠘⢿⣽⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣷⣄⡈⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣷⣶⣤⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⡀⢀⡀⠀⠀⣀⣀⣀⣤⣶⢰⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣦⡐⠳⣶⠲⣖⡶⢲⣇⢻⡇⣤⡙⠿⡋⣷⡉⡷⠙⢂⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣶⣤⢁⣙⠙⠐⣚⣈⣴⣿⣿⣶⣦⣤⣥⣴⣶⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
THEME: CRIMSONTOGGLE PALETTE ›
CYBER DOSSIER

INVESTIGATOR: ANLEN JEBAN (AN1EN) // L LAWLIET

› INITIALIZING OFFENSIVE KERNEL & CIPHERS...0%
[ INITIALIZING RED TEAM INTERFACE ]
[scroll 000%]
[ 0xDEAD ]•OFFENSIVE CYBERSECURITY & RED TEAM PORTFOLIO

CYBER DOSSIER

Active Directory attack chains, security audits, and offensive tooling by Anlen Jeban (AN1EN).

L LAWLIET // INVESTIGATOR CODEX
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠛⠋⠉⠉⣨⣽⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠁⠀⠀⠀⠀⣠⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⠋⠀⠀⠀⠀⠀⠀⠰⠟⠻⠛⠛⠛⠻⠿⠿⢿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⠿⠿⠛⠛⠋⠉⠉⠉⠙⠃⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠉⠙⠻⢿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠟⣋⣀⣤⣤⡤⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣩⣼⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢤⣤⣶⣾⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⠏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⢿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠻⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠀⠀⠀⢀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣃⡔⠀⠀⠀⠀⠀⡰⠊⠡⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢹⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠠⡐⠁⠀⢀⠡⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿
⣿⣿⣿⣿⣿⡟⠁⠀⠀⠀⣠⢷⠀⢿⣟⣿⡇⠂⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢻⣿⣿
⣿⣿⣿⠿⠋⠀⠀⠀⠀⣼⣻⣎⣧⡬⢭⣞⣬⡀⠀⠀⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠸⣿⣿
⣿⣿⣤⣤⣤⣤⡄⠀⠀⣿⣳⡿⠃⣽⣟⣾⣳⠇⠀⠀⠆⠣⠀⠀⢀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿
⣿⣿⣿⣿⣿⣿⣷⠀⠀⢹⣯⢿⣷⣻⣞⡷⣿⢷⢠⠃⠀⠀⣀⠠⣟⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣤⣀⡀⠀⠙
⣿⣿⣿⣿⣿⣿⣿⡆⠀⠀⢿⣇⣈⣷⣿⣻⣽⣯⢷⠈⢟⣿⣻⠶⠈⠖⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢰⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠏⣰⠀⠀⠈⣿⢿⣹⣾⡿⣷⣏⡿⣆⠀⠈⠁⣀⠾⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⣿⣿⠟⣡⣾⣷⠀⡀⢳⣌⠛⢫⣿⡽⣟⣾⡽⣾⡽⣶⣻⡜⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⡿⠃⣼⣟⡷⣷⣾⣷⠘⣾⣿⣦⡈⠙⠛⠷⠿⢳⡿⠷⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣴⣄⠀⠀⠀⣿⣿⣿⣿⣿
⣿⣿⢁⣾⣻⢾⡽⣯⣿⣽⡆⣿⡿⠿⢏⣷⡠⡂⠄⡄⠀⠀⠀⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣷⣤⣀⣘⣿⣿⣿⣿
⣿⠁⣾⣷⠯⠿⠽⠿⠟⠋⢑⡵⣮⢟⡾⣶⠝⠆⠀⠀⠠⣾⣹⡟⣿⣳⣄⠀⠀⠀⠀⢠⣶⡀⠀⠀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠇⢸⢆⣠⣴⣶⣶⣶⡞⢡⡾⠉⠈⠉⠉⠁⠀⠀⠈⠀⠀⠀⠉⠛⠓⠓⢋⡀⠀⠀⢠⣿⣿⣷⣦⣀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠀⣴⣿⣟⣯⢿⣞⣿⠀⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠄⠀⠘⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿
⡄⠻⣿⣟⡾⣯⢿⠟⡄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠐⠠⢠⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡟
⣿⣦⠉⣉⠹⠩⠥⠛⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢲⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⡭⡻⠇⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⣮⣞⡍⠆⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⣿⣼⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣧⠘⢿⣽⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣷⣄⡈⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣷⣶⣤⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⡀⢀⡀⠀⠀⣀⣀⣀⣤⣶⢰⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣦⡐⠳⣶⠲⣖⡶⢲⣇⢻⡇⣤⡙⠿⡋⣷⡉⡷⠙⢂⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣶⣤⢁⣙⠙⠐⣚⣈⣴⣿⣿⣶⣦⣤⣥⣴⣶⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
THEME: CRIMSONTOGGLE PALETTE ›
~/investigation/an1en_dossier.sh
HTB ID
Proving Grounds
SPECIALIST
Active Directory RTS
HTB CPTS
Target Credential
3 AUDITED
Case Studies
SCROLL TO EXPLORE CASE STUDIES & TOOLING
CASE STUDIES•PENTEST AUDITS & LAB WALKTHROUGHS

Root the host.

Hands-on penetration audits, Active Directory attack chains, and proving ground case studies. Every target in this index was compromised, dissected, and documented under rigorous ethical standards.
RULE 0Rule 0: only retired or authorized targets are inscribed.
FEATURED CASE STUDIES3 AUDITED LABS
View All Writeups Archive
SOFTWARE & FRAMEWORKS // OFFENSIVE & AI TOOLING

PROJECTS & TOOLING

PROJ-01
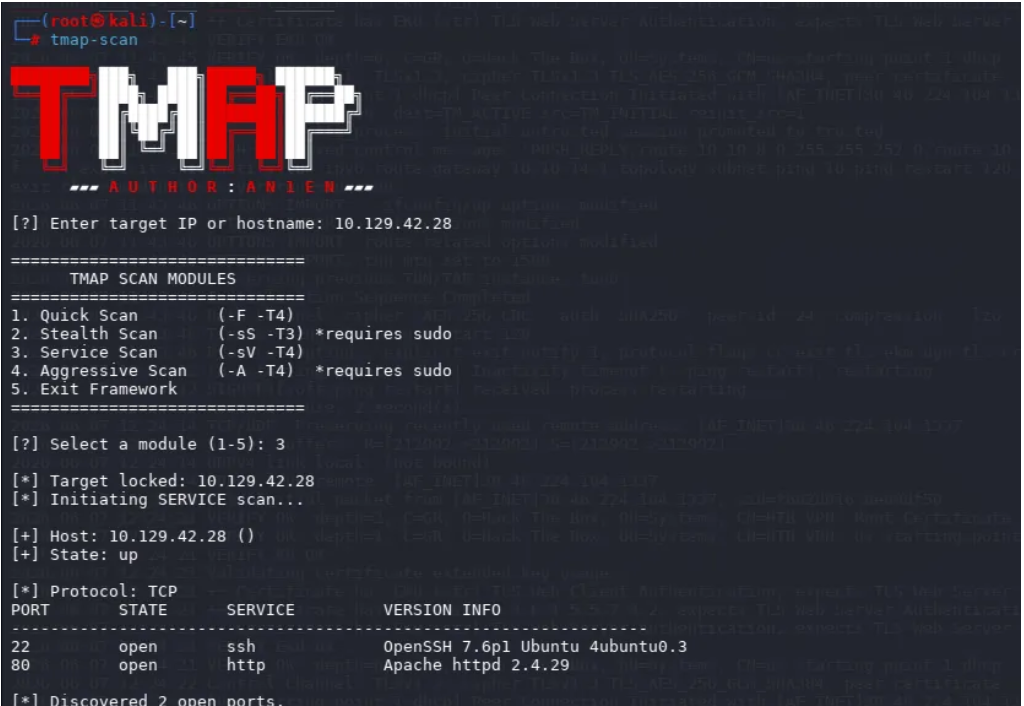
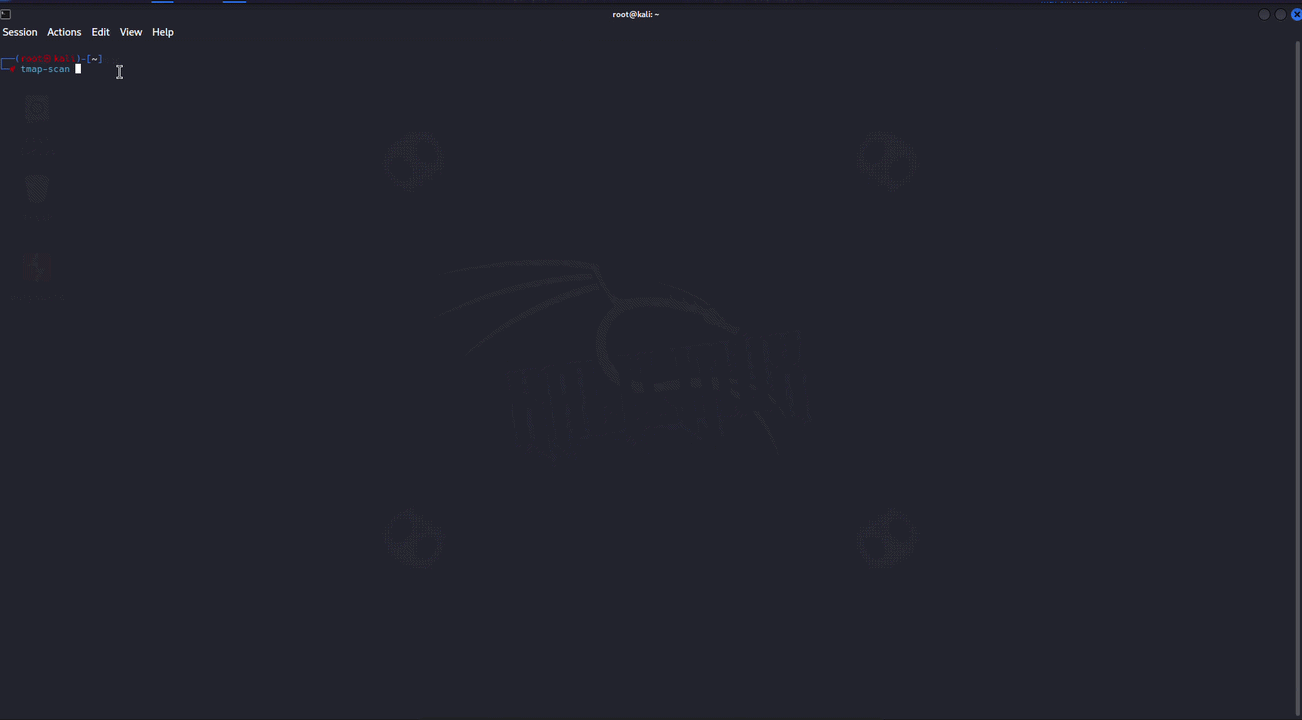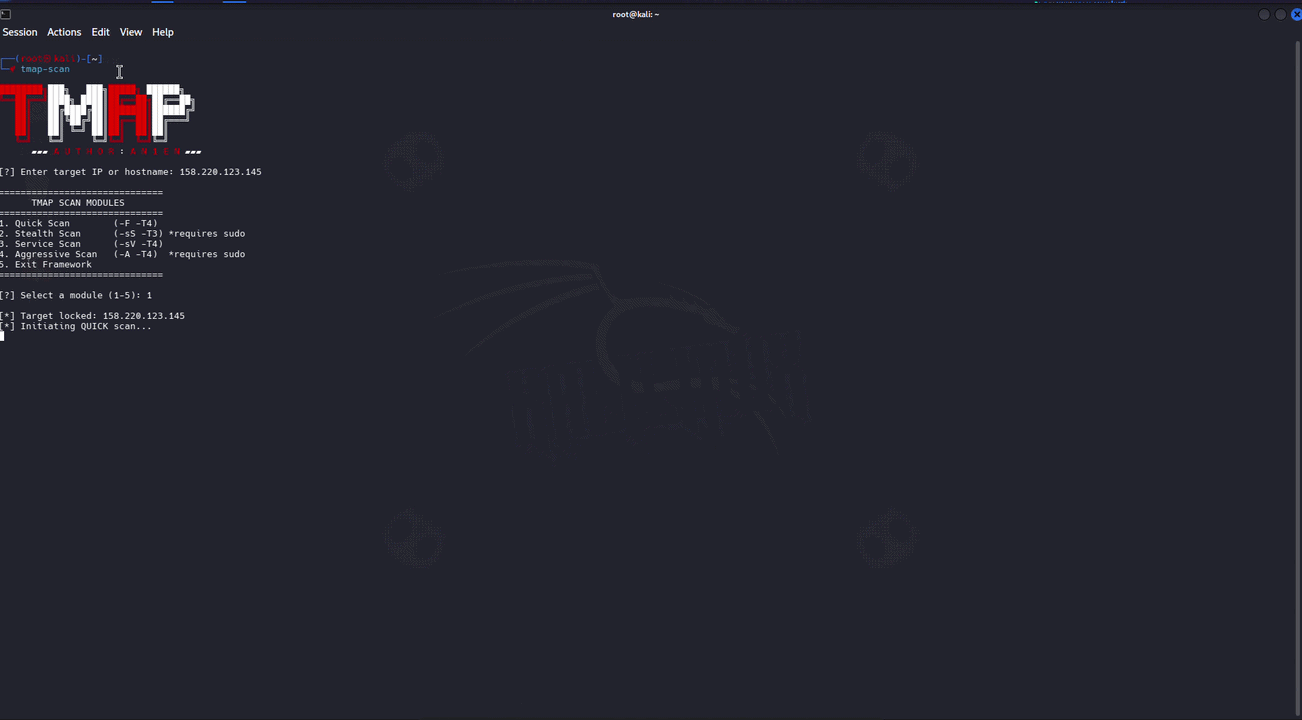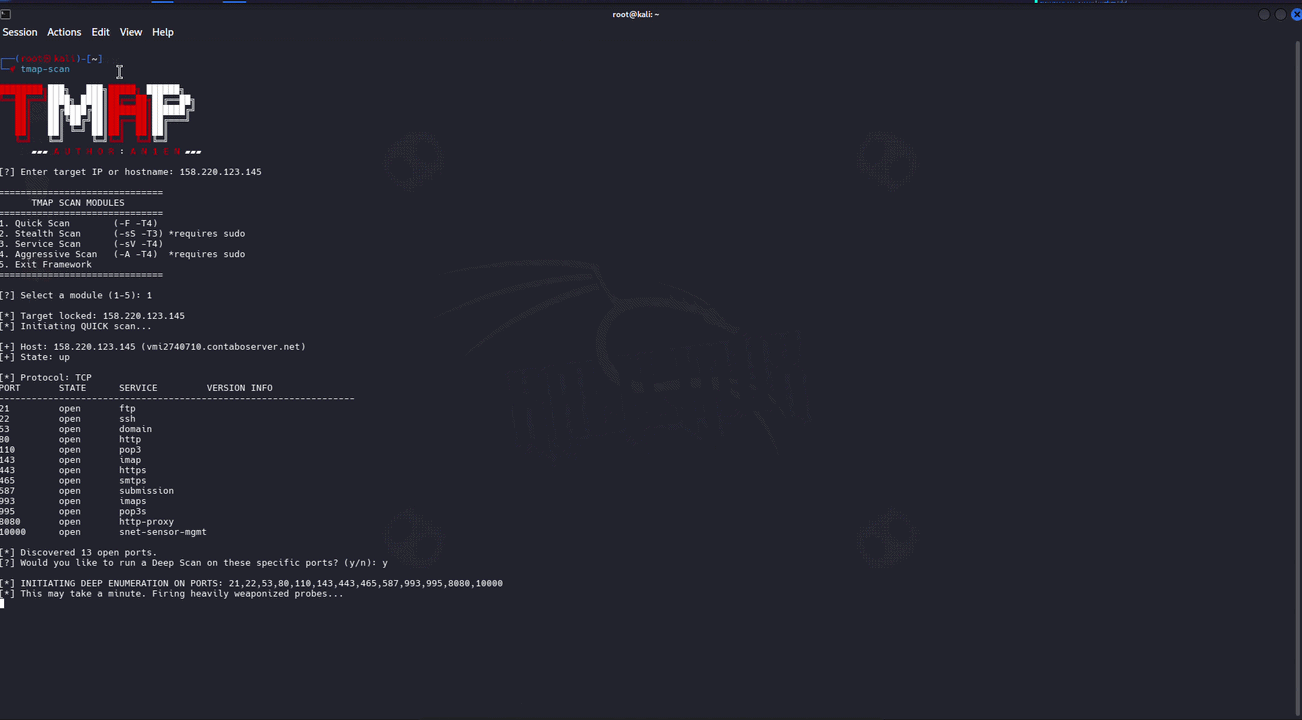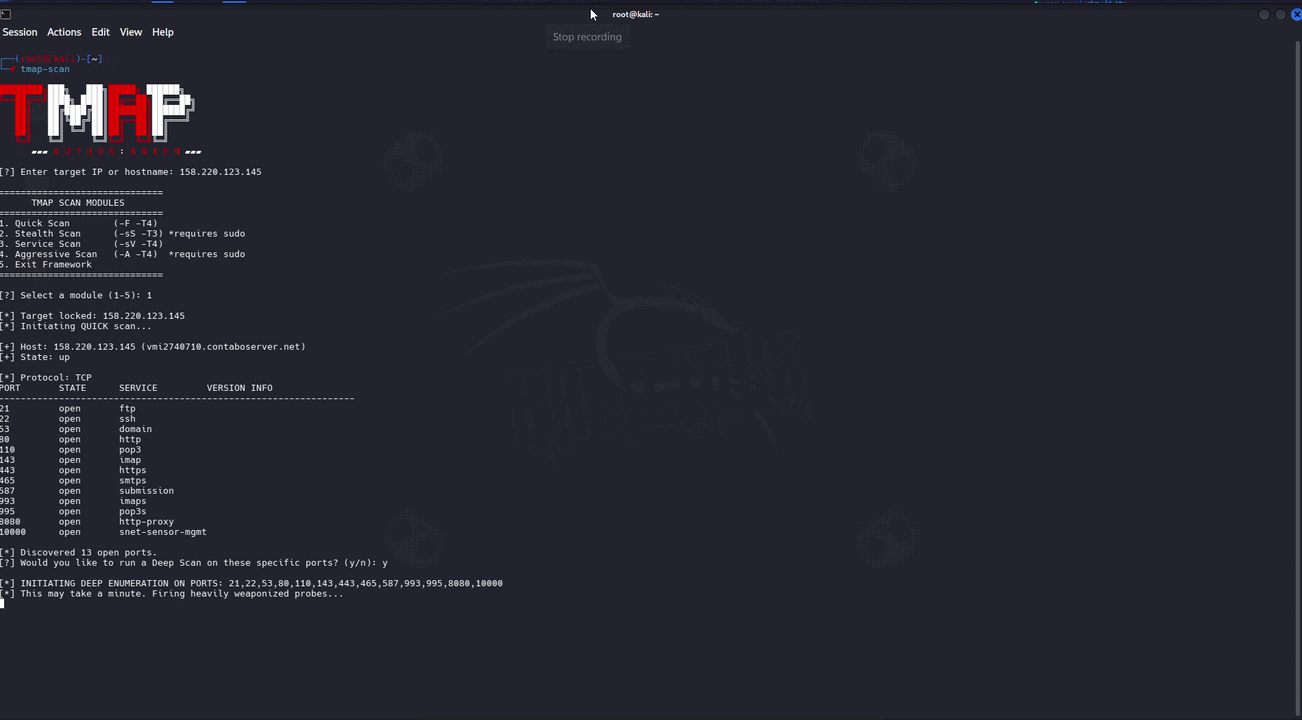
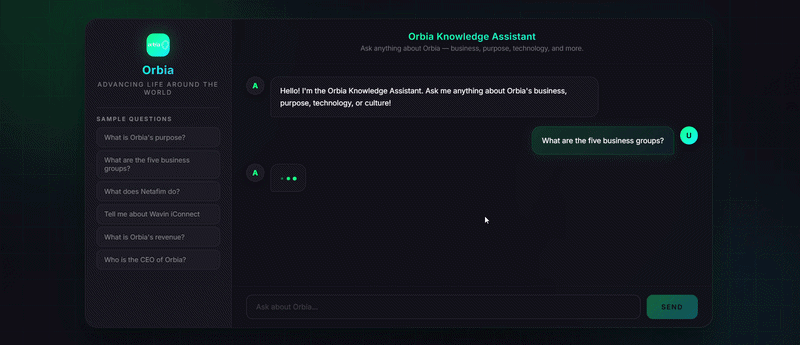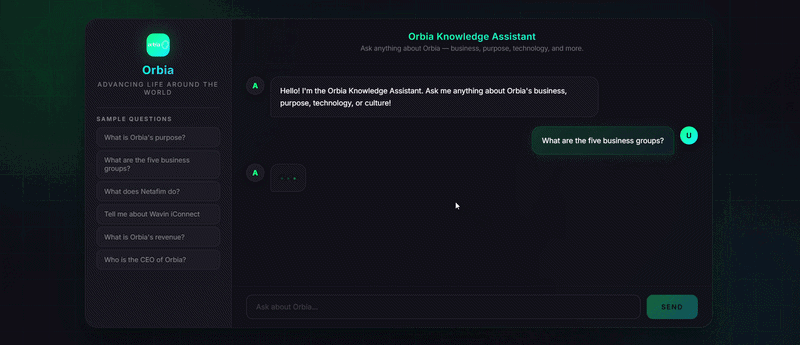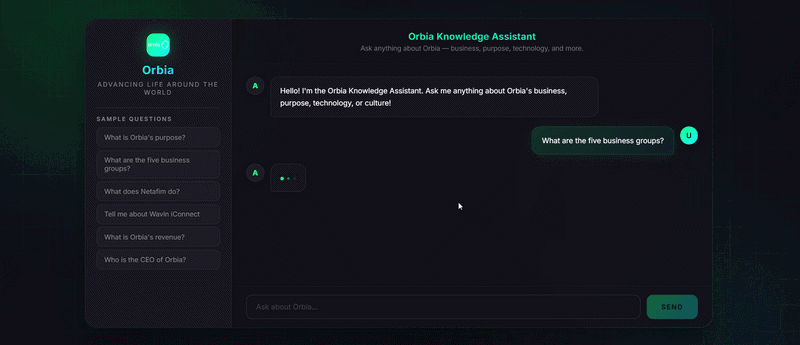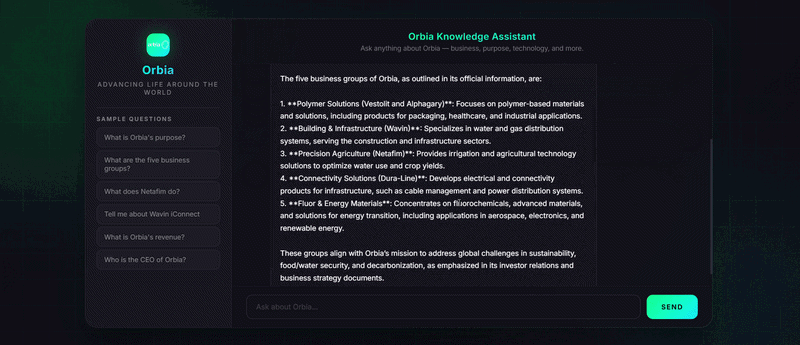
Tmap — Network Recon Framework demo
LIVE PREVIEW

Tmap — Network Recon Framework

Interactive network discovery framework with terminal UI, automated smart port parsing, and deep enumeration workflows across 1000+ ports.
PythonNmapLinuxShell
DEPLOYED
PROJ-02
Orbia RAG Chatbot demo
LIVE PREVIEW

Orbia RAG Chatbot

AI-powered company knowledge assistant using RAG pipeline. Scrapes 50+ documents, chunks into 146 searchable fragments, retrieves context via keyword search, and generates answers via OpenRouter LLM.
PythonFastAPIOpenRouterChromaDBLangChainVercel
DEPLOYED
PROJ-03
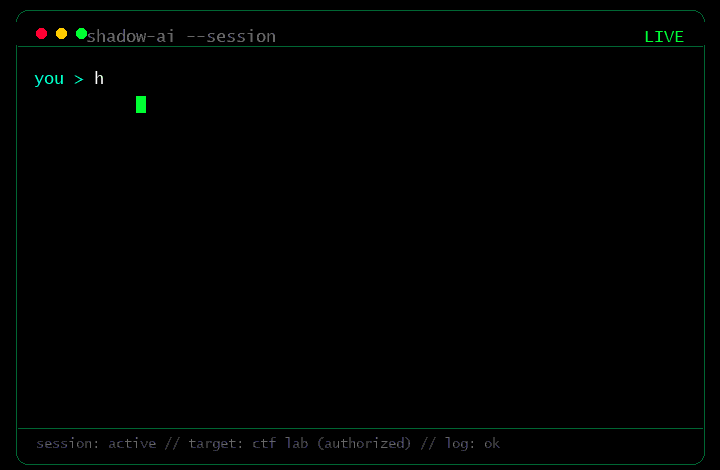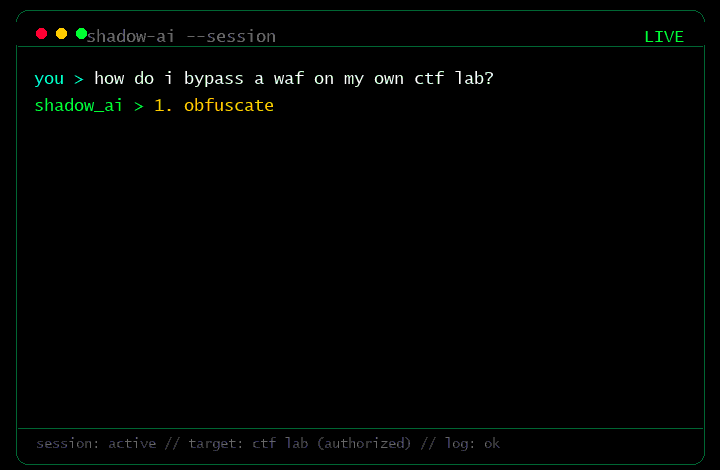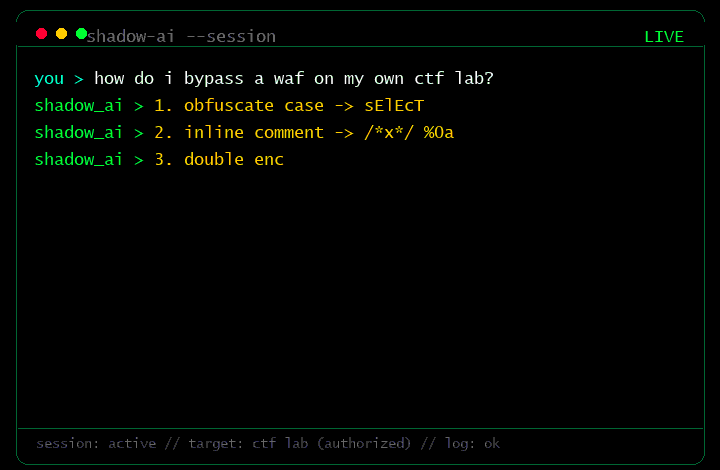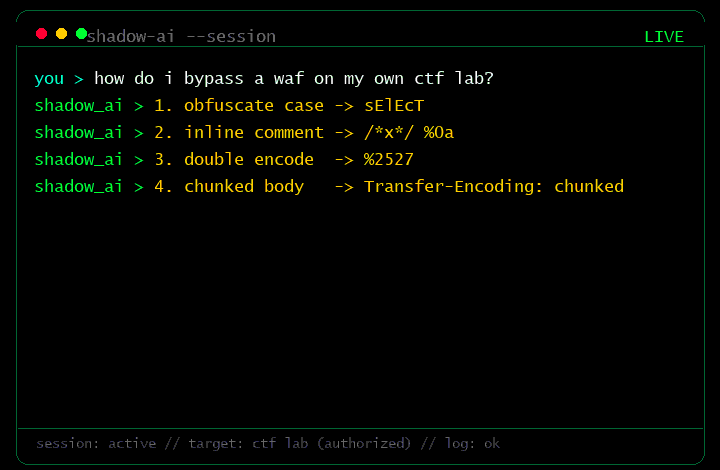
SHADOW AI — CYBERSECURITY PENTESTING ASSISTANT demo
LIVE PREVIEW

SHADOW AI — CYBERSECURITY PENTESTING ASSISTANT

AI-powered cybersecurity pentesting assistant with real-time LLM integration, automated writeup and professional report generation from session data, and intelligent vulnerability analysis and exploit guidance.

Next.jsTypeScriptOpenRouterGPT-4o-miniTailwind CSSVercel
DEPLOYED
PROVING GROUND TELEMETRY // CAPABILITIES

TACTICAL PROFICIENCIES

Verify HTB Offense Radar
›Red Team & Exploitation
†Active Directory†Kerberoasting†ESC1 Certificate Abuse†BloodHound†Metasploit†Mimikatz†Burp Suite Pro
›Reconnaissance & OSINT
†Tmap†Nmap†Maltego†Spiderfoot†Recon-ng†Shodan†Wireshark
›Systems & Security Engineering
†Linux Administration†Bash Scripting†Python†SELinux†Docker†FastAPI†TypeScript†Next.js
›Cryptography & Theory
†PKI & Encryption†Quantum Safe Methods†Symmetric/Asymmetric Ciphers†Hashing†MITRE ATT&CK
CREDENTIAL VERIFICATION // ATTESTATION

CREDENTIALS

PREP IN PROGRESS

Certified Penetration Testing Specialist (CPTS)

Hack The Box Academy • ACTIVE PREP // 2026
Full Network PentestingActive Directory AttacksWeb AssessmentPivoting & Tunneling
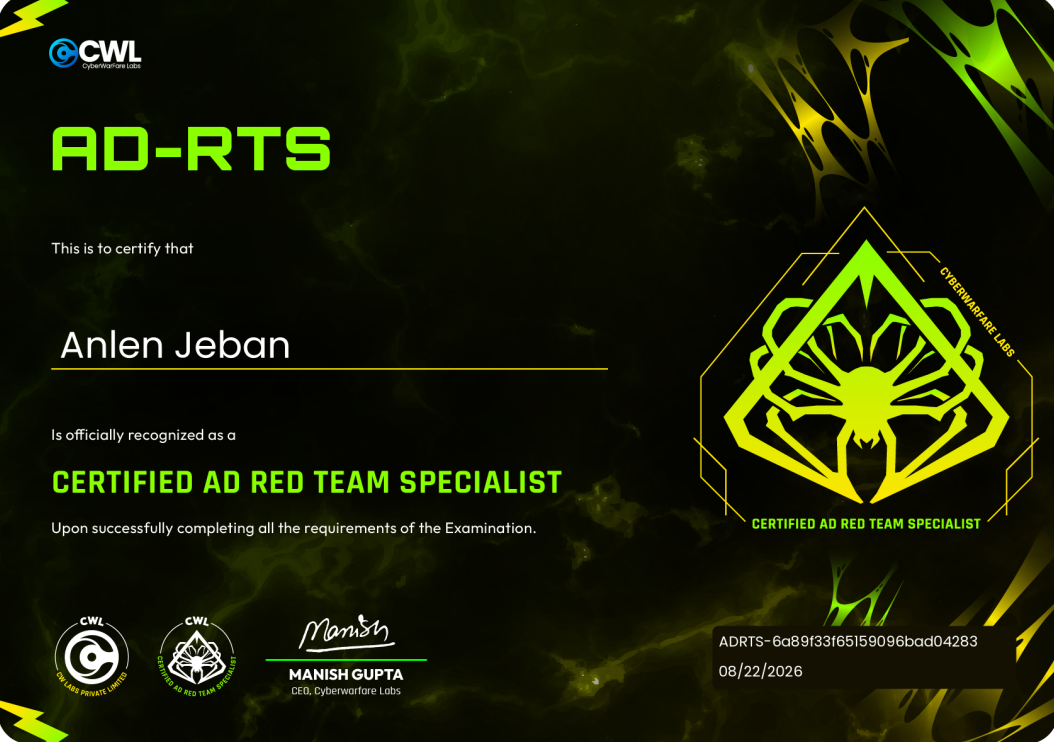
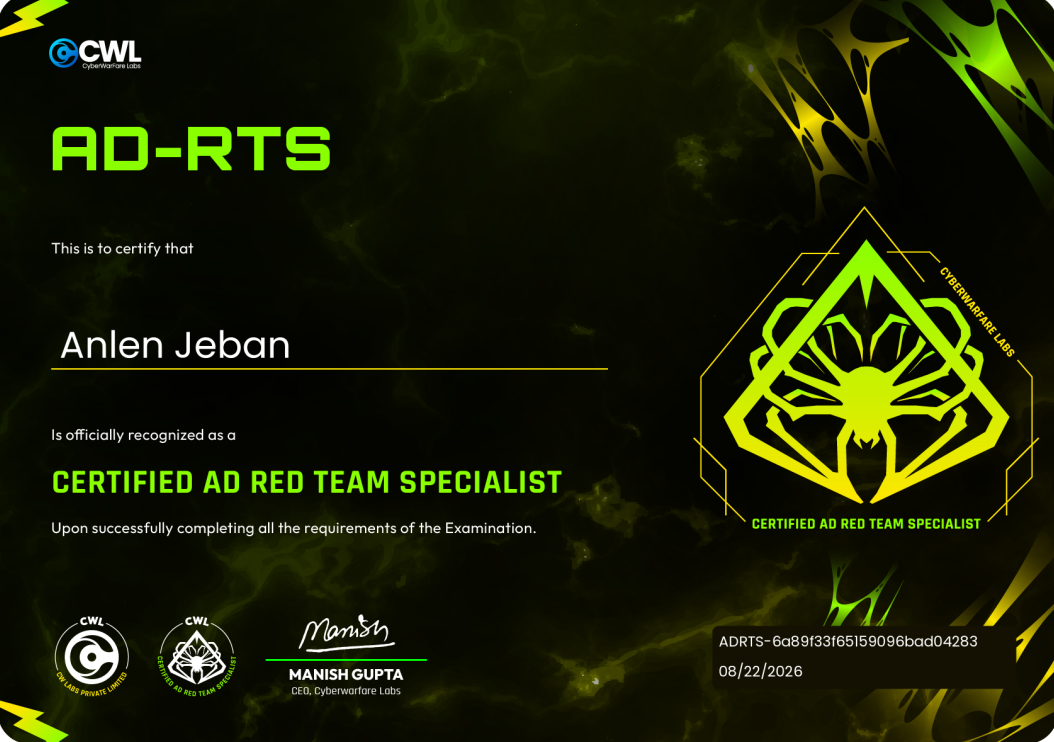
Active Directory Red Team Specialist (AD-RTS)
CRYPTOGRAPHICALLY VERIFIED
verify

Active Directory Red Team Specialist (AD-RTS)

Cyberwarfare Labs • 2026ID: 6a89f33f65159096bad04283
AD ExploitationCertificate ServicesExchange AttacksLateral Movement
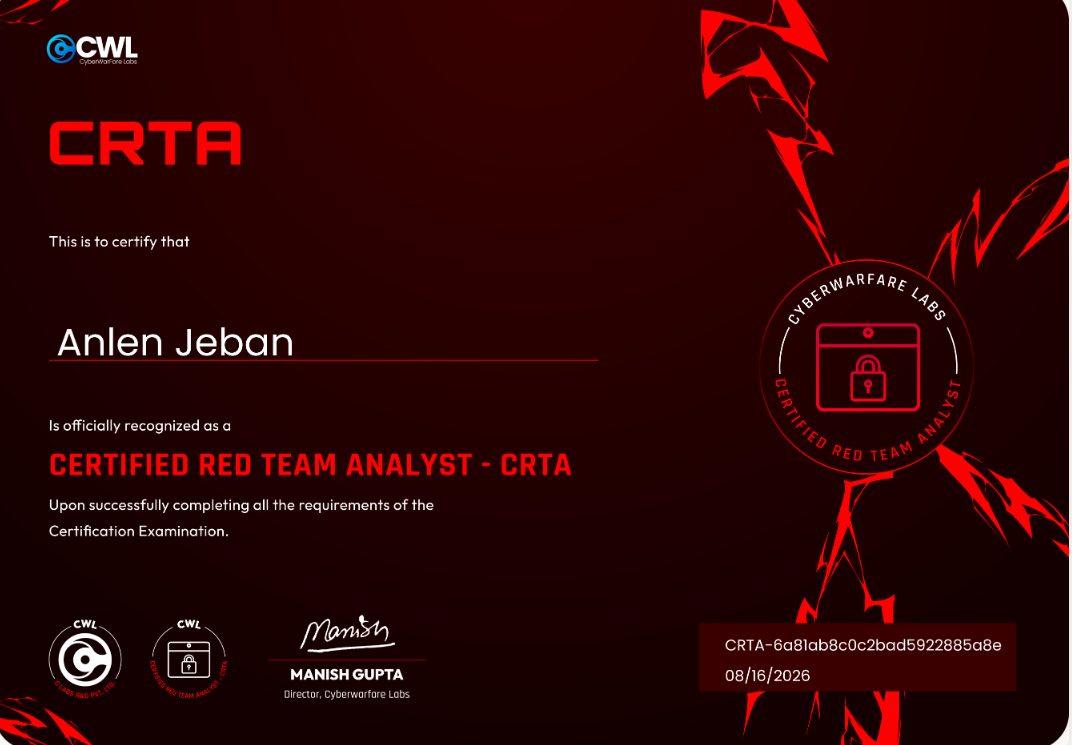
Certified Red Team Analyst (CRTA)
CRYPTOGRAPHICALLY VERIFIED
verify

Certified Red Team Analyst (CRTA)

Cyberwarfare Labs • 2026ID: 6a81ab8c0c2bad5922885a8e
Red TeamingMITRE ATT&CKActive DirectoryPentesting
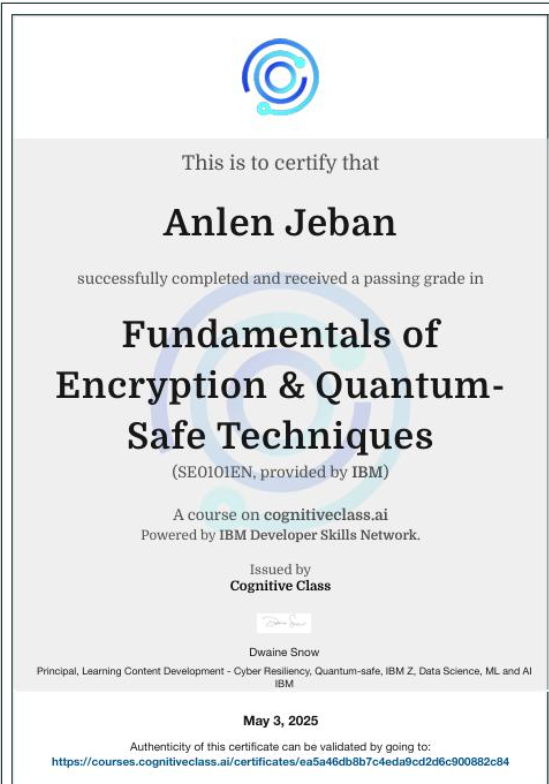
Fundamentals of Encryption & Quantum Safe Techniques
CRYPTOGRAPHICALLY VERIFIED
verify

Fundamentals of Encryption & Quantum Safe Techniques

IBM — Cognitive Class • 2025
CryptographyEncryptionData SecuritySymmetric/Asymmetric Encryption
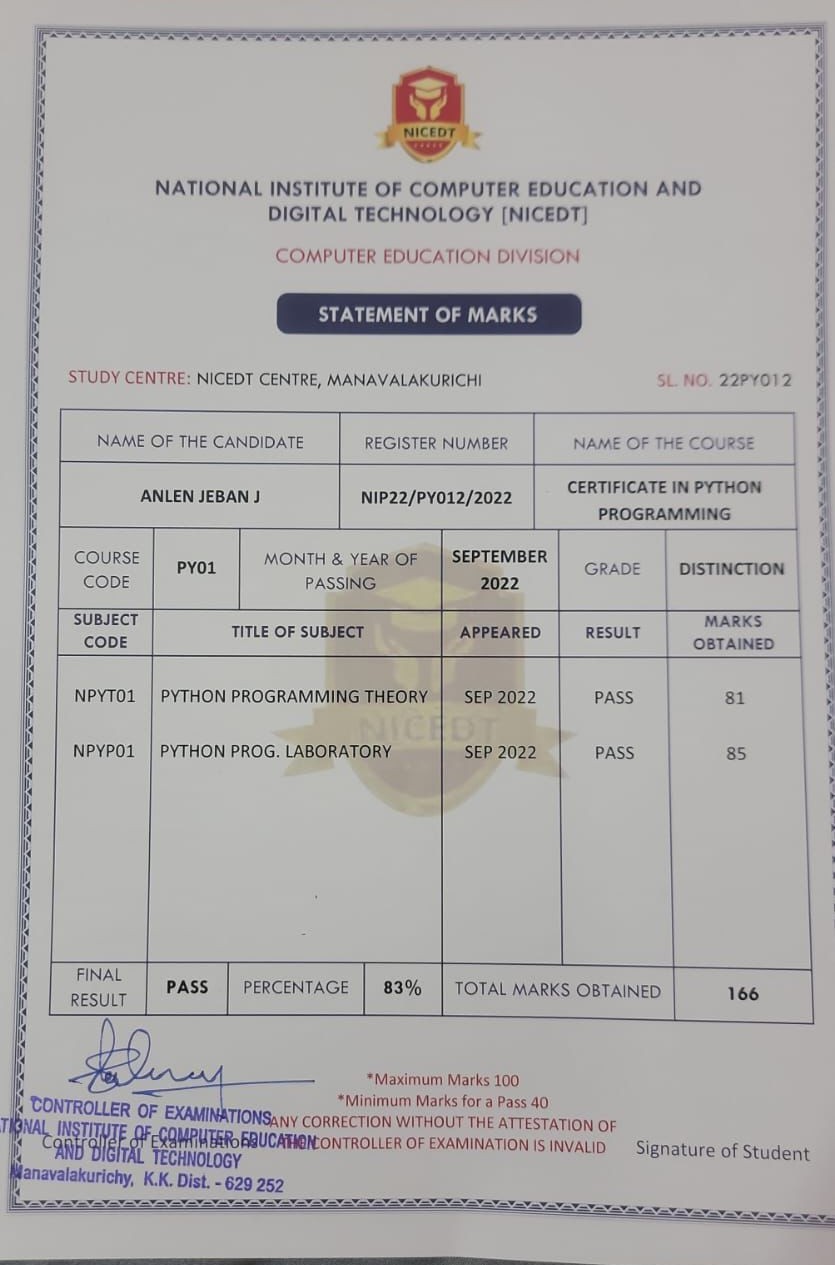
Python Programmer
CRYPTOGRAPHICALLY VERIFIED

Python Programmer

NICEDT • 2025

PythonObject-Oriented ProgrammingData StructuresScripting
RULES OF ENGAGEMENT // NOTE MANUAL

HOW TO USE IT

Strict operational guidelines governing vulnerability discovery, exploitation mechanics, and ethical disclosures.

RULE 0SEC_CLAUSE // 0x01

RULE 0: AUTHORIZED ENGAGEMENT

“Rule 0: only retired or authorized targets are inscribed. The offensive researcher possessing this dossier operates strictly under authorized rules of engagement, certified proving grounds, and responsible disclosure standards.”

STATUS: CODIFIED
RULE ISEC_CLAUSE // 0x02

PERIMETER PENETRATION

“The host whose hostname, IP address, or domain is inscribed within this dossier shall have its security architecture enumerated, mapped, and audited without leaving anomalous forensic attribution.”

STATUS: CODIFIED
RULE IISEC_CLAUSE // 0x03

PRIVILEGE ESCALATION

“Attaining domain administrative or root authority takes effect within 40 seconds of memory harvesting, ticket forging, or token impersonation.”

STATUS: CODIFIED
RULE IIISEC_CLAUSE // 0x04

LATERAL TRAVERSAL

“Unless the specific vector of compromise is designated beforehand, the target machine shall succumb to automated lateral movement and kernel exploitation.”

STATUS: CODIFIED
RULE IVSEC_CLAUSE // 0x05

ETHICAL COVENANT

“Every vulnerability inscribed into this codex is verified against isolated lab environments with zero disruption to external networks.”

STATUS: CODIFIED
KIRA NOTEBOOK // TARGET EXECUTION ENGINE

DEATH NOTE

The human or system whose name is written in this note shall be rooted. Enter the name of the target you wish to destroy.

RULE I // EXECUTION PROTOCOL

HOW TO USE: TYPE TARGET NAME

Once inscribed, the penetration testing sequence begins in 40 seconds.

Max 32 characters • Real-time ink animation0/32
QUICK INSCRIBE:
DEATH NOTE ARCHIVE RECORD LEDGERLIVE SYNC
REC-012026-10-16
Light Yagami (Kira)
Forensic Attribution // Keystroke Telemetry & Network Exposure
REC-022026-10-16
L Lawliet
Memory Dump & Keystroke Attribution Discovery
REC-032026-10-16
Lind L. Tailor
Broadcast Transmission Interception & Subnet Honeypot Trap
REC-042026-10-15
Raye Penber
Ticket Forgery & Subway Terminal Compromise
REC-052026-10-15
Naomi Misora
Zero-Trace Covert De-anonymization & Identity Zeroization
REC-062026-10-15
Kyosuke Higuchi
Yotsuba Executive Insider Privilege Escalation

GET IN TOUCH // CONTACT

~/contact.sh --pgp --interactive