SYSTEM_LOAD // 0xDEADCLICK ANYWHERE TO ENTER ›
L LAWLIET // INVESTIGATOR CODEX
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠛⠋⠉⠉⣨⣽⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠟⠁⠀⠀⠀⠀⣠⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⠋⠀⠀⠀⠀⠀⠀⠰⠟⠻⠛⠛⠛⠻⠿⠿⢿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⠿⠿⠛⠛⠋⠉⠉⠉⠙⠃⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠉⠙⠻⢿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠟⣋⣀⣤⣤⡤⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣩⣼⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢤⣤⣶⣾⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⠏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⢿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠈⠻⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠀⠀⠀⢀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠙⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣃⡔⠀⠀⠀⠀⠀⡰⠊⠡⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢹⣿⣿⣿
⣿⣿⣿⣿⣿⣿⡿⠀⠀⠀⠀⠠⡐⠁⠀⢀⠡⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿
⣿⣿⣿⣿⣿⡟⠁⠀⠀⠀⣠⢷⠀⢿⣟⣿⡇⠂⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢻⣿⣿
⣿⣿⣿⠿⠋⠀⠀⠀⠀⣼⣻⣎⣧⡬⢭⣞⣬⡀⠀⠀⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠸⣿⣿
⣿⣿⣤⣤⣤⣤⡄⠀⠀⣿⣳⡿⠃⣽⣟⣾⣳⠇⠀⠀⠆⠣⠀⠀⢀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿
⣿⣿⣿⣿⣿⣿⣷⠀⠀⢹⣯⢿⣷⣻⣞⡷⣿⢷⢠⠃⠀⠀⣀⠠⣟⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣤⣀⡀⠀⠙
⣿⣿⣿⣿⣿⣿⣿⡆⠀⠀⢿⣇⣈⣷⣿⣻⣽⣯⢷⠈⢟⣿⣻⠶⠈⠖⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢰⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⠏⣰⠀⠀⠈⣿⢿⣹⣾⡿⣷⣏⡿⣆⠀⠈⠁⣀⠾⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⣿⣿⠟⣡⣾⣷⠀⡀⢳⣌⠛⢫⣿⡽⣟⣾⡽⣾⡽⣶⣻⡜⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢸⣿⣿⣿⣿⣿
⣿⣿⡿⠃⣼⣟⡷⣷⣾⣷⠘⣾⣿⣦⡈⠙⠛⠷⠿⢳⡿⠷⠋⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣴⣄⠀⠀⠀⣿⣿⣿⣿⣿
⣿⣿⢁⣾⣻⢾⡽⣯⣿⣽⡆⣿⡿⠿⢏⣷⡠⡂⠄⡄⠀⠀⠀⣀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣷⣤⣀⣘⣿⣿⣿⣿
⣿⠁⣾⣷⠯⠿⠽⠿⠟⠋⢑⡵⣮⢟⡾⣶⠝⠆⠀⠀⠠⣾⣹⡟⣿⣳⣄⠀⠀⠀⠀⢠⣶⡀⠀⠀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠇⢸⢆⣠⣴⣶⣶⣶⡞⢡⡾⠉⠈⠉⠉⠁⠀⠀⠈⠀⠀⠀⠉⠛⠓⠓⢋⡀⠀⠀⢠⣿⣿⣷⣦⣀⠀⢸⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⠀⣴⣿⣟⣯⢿⣞⣿⠀⡏⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠄⠀⠘⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡿
⡄⠻⣿⣟⡾⣯⢿⠟⡄⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠐⠠⢠⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⡟
⣿⣦⠉⣉⠹⠩⠥⠛⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢲⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⡭⡻⠇⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⣮⣞⡍⠆⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⠀⢸⣿⣼⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠹⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣧⠘⢿⣽⡀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢀⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣷⣄⡈⠁⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⠀⢺⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣷⣶⣤⠀⡀⠀⠀⠀⠀⠀⠀⠀⠀⡀⢀⡀⠀⠀⣀⣀⣀⣤⣶⢰⣾⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣦⡐⠳⣶⠲⣖⡶⢲⣇⢻⡇⣤⡙⠿⡋⣷⡉⡷⠙⢂⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣶⣤⢁⣙⠙⠐⣚⣈⣴⣿⣿⣶⣦⣤⣥⣴⣶⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿⣿
THEME: CRIMSONTOGGLE PALETTE ›
CYBER DOSSIER

INVESTIGATOR: ANLEN JEBAN (AN1EN) // L LAWLIET

› INITIALIZING OFFENSIVE KERNEL & CIPHERS...0%
[ INITIALIZING RED TEAM INTERFACE ]
TECHNICAL ARCHIVE // DECLASSIFIED SECURITY AUDITS

SECURITY WRITEUPS

In-depth technical penetration testing walkthroughs, Active Directory attack chains, and proving ground machine post-mortems.

RULE 0Rule 0: only retired or authorized targets are inscribed.
STATUS: 3 TECHNICAL WRITEUPS AVAILABLE
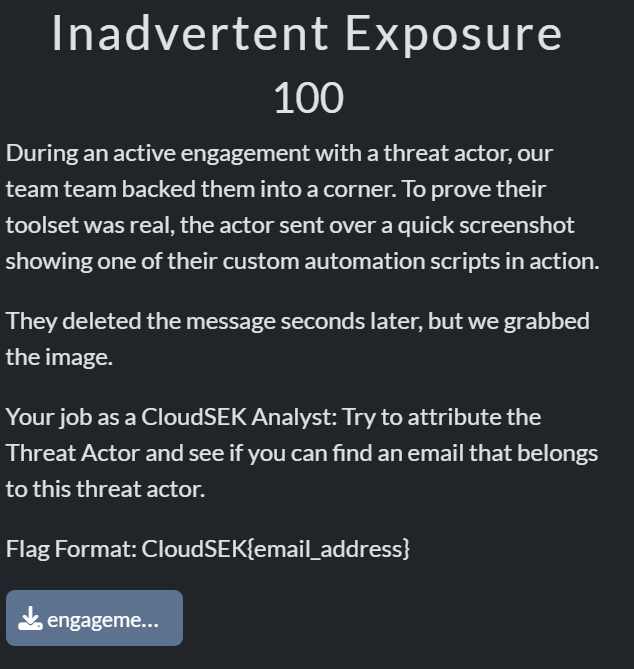
CloudSEK CTF 2026 — OSINT & Web Security
CASE-001CloudSEK CTF • Aug 2026
Threat: ElevatedCASE CLOSED
CASE-001 · CloudSEK CTF: StrikeVigil

CloudSEK CTF 2026 — OSINT & Web Security

Time to root: 2h 45m
Kill ChainUsername Recon → GitHub API Leak → Host Header Poisoning → Password Reset → Admin RCE

Comprehensive writeup covering OSINT reconnaissance through username enumeration and GitHub API exploitation, plus web security attacks including Host header injection and password reset poisoning for full admin account takeover.

OSINTWeb SecurityCTFHost Header InjectionPassword Reset Poisoning
AD RTS — TELECOM INC: Full Attack Chain
CASE-003Cyberwarfare Labs • Jul 2026
Threat: CriticalROOTED
CASE-003 · AD RTS: Telecom Inc.

AD RTS — TELECOM INC: Full Attack Chain

Time to root: 6h 40m
Kill ChainLDAP → AS-REP → Exchange → GodPotato → ESC1 → ESXi

Complete attack chain against an Active Directory environment — from anonymous LDAP enumeration and AS-REP Roasting through Exchange impersonation, GodPotato privilege escalation, ESC1 certificate abuse, to VMware ESXi hypervisor compromise.

Active DirectoryRed TeamLateral MovementESC1Privilege Escalation
HackTheBox — Oopsie Walkthrough
CASE-002HackTheBox • Jun 2026
Threat: LowROOTED
CASE-002 · HTB: Oopsie Linux

HackTheBox — Oopsie Walkthrough

Time to root: 1h 15m
Kill ChainTmap Port Scan → IDOR Cookie Hijack → PHP Reverse Shell → SUID PATH Hijack → Root

Detailed analysis of IDOR, Unrestricted File Upload, and SUID PATH Hijacking vulnerabilities with full exploitation chain and remediation strategies.

IDORReverse ShellPATH HijackingOWASP Top 10
3
Case Files
3
Proving Platforms
100%
Proof of Concept